01
Accountable ownership
Keep the current owner, next action and case context visible through team handoffs.

Regulated customer operations
Bring complaints, cases, incidents and escalations into a clear operating workflow. Connect accountable owners, response targets and evidence across team handoffs.
Regulatory complaint management software helps organizations capture complaints, assign accountable owners, track response deadlines, document investigations and decisions, organize evidence, manage escalation and identify recurring issues. It supports an organization's compliance process but does not replace legal advice, regulatory interpretation or a full governance, risk and compliance (GRC) platform. Exact capabilities depend on the product and agreed implementation.
Where ResolveCX helps
Four practical foundations for complaint, case, incident and escalation operations.
Keep the current owner, next action and case context visible through team handoffs.
Bring agreed target dates and review points into the work, alongside each matter.
Keep investigation notes, correspondence and decisions with the case they support.
People assess applicability, exceptions, reportability and regulated outcomes.
ResolveCX is not a full GRC platform, legal interpretation service, regulatory intelligence feed, obligation library, control-mapping system, enterprise audit platform or certification service.
Suggested organizational workflow
Ten stages to adapt to your organization. People remain accountable for regulatory interpretation and decisions.
At each handoff
Define the information that distinguishes a complaint, inquiry or incident, and agree the intake fields.
Set response targets against approved policies, with clear ownership for review.
Keep findings, decision rationale and response records in the context of the matter.
Categories may inform configured routing or escalation; people own exceptions and regulated decisions.
Review recurring themes, investigate root causes and assign follow-up.
Agree what complaint or incident context the team needs and identify the source of the concern.
AI Classification categorizes inbound cases, complaints and inquiries to inform configured team routing or escalation. People handle exceptions.
Qualified people determine the relevant jurisdiction, legal scope and any reporting responsibility.
Name an accountable owner and agree a response target and escalation path under approved procedures.
Gather relevant evidence and distinguish reported concerns from verified findings.
Authorized people decide the outcome, response and any notification, with a clear rationale.
Bring overdue or high-risk matters to the responsible team for human review.
Communicate the authorized response and keep a record of what was communicated.
Check that the response and required organizational follow-up are complete before closure.
Review recurrence, investigate root causes and assign corrective work with an agreed follow-up.
Framework directory
Use each guide as an orientation point; confirm applicability with qualified counsel or your compliance team.
EU GDPR; UK GDPR requires separate review
01Separate supervisory-authority complaints, data subject rights requests, and personal data breach assessment. Review EU and UK applicability separately.
Directory entry 1 of 7California consumer privacy
02Distinguish requests to know, delete or correct from opt-out and limitation requests. Keep security incidents and breach review separate.
Directory entry 2 of 7UK financial services
03Review complaint ownership, response targets and Ombudsman pathways under FCA DISP, including separate EMD and PSD complaint rules.
Directory entry 3 of 7UK communications providers
04Ofcom GC C4 complaint handling, six-week ADR access for relevant complaints raised on or after 8 April 2026, ADR Letters and provider responsibilities.
Directory entry 4 of 7England: CQC-regulated health and social care
05Review Duty of Candour records and communications under CQC Regulation 20. NHS England PSIRF is a separate patient safety response framework.
Directory entry 5 of 7United States: covered entities and business associates
06Distinguish covered entity and business associate responsibilities, breach assessment and notification pathways based on the affected population.
Directory entry 6 of 7International quality management
07Explore complaint evidence, nonconformity investigation, root cause and corrective action within quality management. Software does not establish conformity or certification.
Directory entry 7 of 7Illustrative contexts
Examples of workflow context, not customer proof or claims of regulatory coverage.
Bring complaint ownership and review points into view across customer-facing teams.
Coordinate complaint handling and specialist escalation across service operations.
Keep CQC Regulation 20 Duty of Candour distinct from NHS England PSIRF learning responses and US HIPAA breach responsibilities.
Review complaint evidence alongside nonconformity investigation and corrective work. ISO 9001 conformity and certification need separate assessment.
Separate GDPR supervisory complaints, rights requests and breach assessment; CCPA request types and security review need distinct assessment.
For your evaluation
Use a product review to test the handoffs, records and responsibilities that matter to your organization.
Questions and answers
It is software for managing complaint intake, ownership, investigation, response, escalation and records within an organization's approved procedures. It supports the compliance process, but qualified people remain responsible for legal interpretation and regulated decisions.
ResolveCX focuses on the operational work of complaints, cases, incidents and escalations. Legal interpretation, regulatory intelligence, obligation libraries, control mapping, enterprise audit management and certification sit outside that operating layer.
ResolveCX brings complaint handling, case ownership, response targets and escalation into governed workflows. A workflow review connects your requirements to the records, handoffs and controls available in the product.
ResolveCX supports configurable response targets. Your qualified reviewers establish the applicable FCA DISP path, including general and EMD or PSD complaints. Review timing and exception requirements with the team before agreeing the implementation.
Review unresolved complaints, customer communications and current alternative dispute resolution eligibility with a qualified owner. The Ofcom guide links to official guidance on the applicable path. Eligibility and referral decisions remain with your organization.
Separate GDPR supervisory-authority complaints, data subject requests and breach assessment, with EU and UK applicability reviewed separately. Under CCPA, distinguish request types such as know, delete, correct, opt-out and limit. Security and breach review require their own legal assessment.
CQC Regulation 20 concerns Duty of Candour in England's regulated health and social care. NHS England PSIRF is a separate patient safety response framework. US HIPAA has distinct covered entity, business associate and breach notification responsibilities.
Use a product review to walk through decision history and evidence handling. Ask the team to demonstrate the user records, timestamps, permissions, retention, versioning and export capabilities your organization requires.
Recurring themes can inform problem management and root-cause investigation. Assign responsibility for corrective work and agree how your team will assess the follow-up. Review any record-linking or effectiveness requirements during product evaluation.
No. ResolveCX supports organization-configured workflows and does not provide legal advice or guarantee compliance. The organization remains responsible for applicability, regulatory interpretation, decisions and its compliance controls.
Connected workflows
Explore related operations and ResolveCX Intelligence capabilities.
Start with the work you have
Walk through ownership, response targets, evidence and handoffs with your team.
Keep exploring
Relevant guides and real-world perspectives for the work you are doing now.
 Solution
A destination for financial services teams exploring complaint management in the context of their industry.
Explore resourceSolutionA destination for teams exploring complaint management in the context of FCA-related requirements.
Explore resource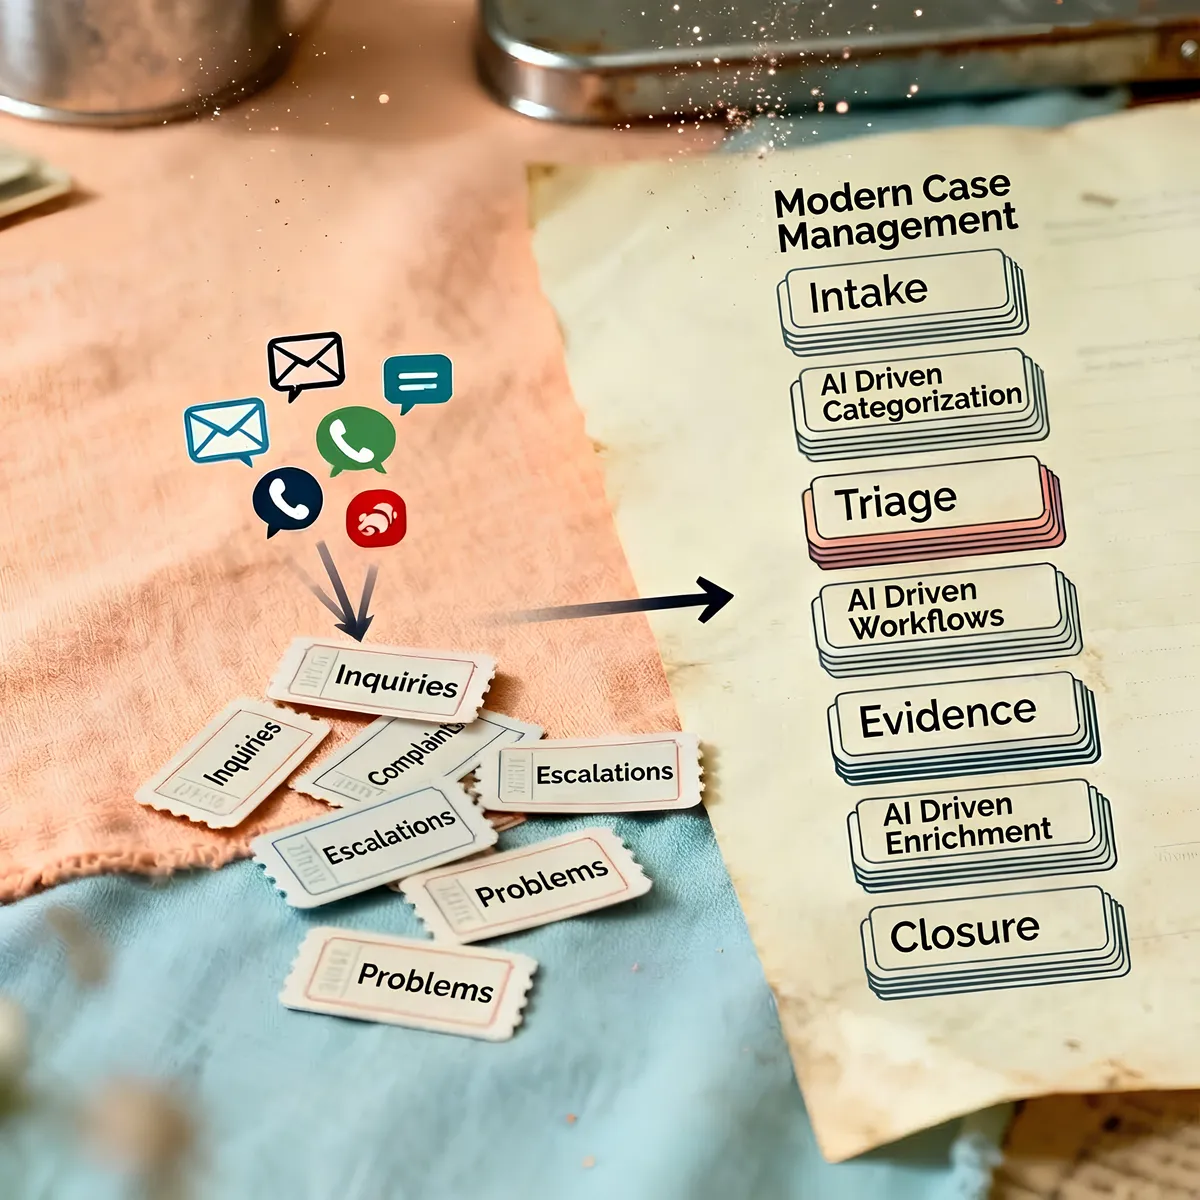 Solution
A destination for healthcare service teams exploring incident management in the context of CQC-related requirements.
Explore resourceSolutionA destination for healthcare service teams exploring incident management in the context of HIPAA-related requirements.
Explore resource Blog
Practical thinking on complaint governance, escalation management, and case resolution for regulated industries.
Explore article Video
Capture, investigate, govern and resolve complaints from intake to verified closure.
Explore videoCase studySee how regulated healthcare teams improved SLA adherence, reduced escalations, and accelerated audit preparation.
Explore resourceFollow the latest ResolveCX updates, governance conversations, and practical customer operations insights.
Explore resource